Security & compliance
Enterprise-grade
trust & security
The Varcio platform is built with security at every layer — from credential encryption to immutable audit trails and compliance control mapping.
Core principles
Security by design, not afterthought
Four foundational principles guide every architectural and product decision.
Zero trust by default
No implicit access. Every API call is authenticated, authorized, and rate-limited.
No plaintext secrets
AWS uses AssumeRole, while Azure, GCP, and OCI credentials are encrypted at rest and never exposed in logs, API responses, or the UI.
Immutable audit trail
Every action, decision, and data access is logged with actor, timestamp, payload, and outcome. Logs cannot be modified or deleted.
Defense in depth
Multiple independent security layers — authentication, authorization, execution safety, rate limiting, and protected resources.
Defense in depth
Four layers around every cost action
Credentials never sit in plaintext, permissions are scoped twice, and every write passes human approval or Autopilot’s confidence and budget limits before it reaches a resource.
Approval pipeline
From finding to action, fully audited
Detection is automated. Action clears policy and a named approver first, unless you turn on Autopilot, which acts only above confidence thresholds and within a monthly budget.
Data flow
How your data moves through the platform
From connection to action — every step is encrypted, audited, and gated.
Connect
Provider-native trust models with no plaintext credential exposure
AWS: AssumeRole with External ID. Azure: encrypted Service Principal. GCP: encrypted service account key with short-lived tokens. OCI: encrypted API signing key.
Ingest
Cost data pulled via official cloud APIs
AWS Cost Explorer and Cost and Usage Report, Azure Cost Management, GCP BigQuery billing export and the OCI Usage API — read with read-only access.
Process
Data normalized, analyzed, and stored encrypted
Cost metadata is encrypted at rest, encrypted in transit, and processed inside isolated application environments.
Act
Remediation runs behind approval and guardrails
Requested changes need approval; Autopilot, if enabled, acts only above confidence thresholds and within a monthly action budget. Protected tags exclude critical resources, and rollout-safety gates can hold a run to dry run.
Controls
9 security control layers
Every layer of the platform is designed with defense-in-depth principles.
Authentication
JWT sessions, OAuth (Google, GitHub, Azure AD), SSO via OIDC and SAML 2.0, SCIM provisioning (Enterprise)
Authorization
Dual-layer RBAC: page permissions (navigation) + action permissions (operations)
Credential storage
AWS KMS envelope encryption: each record gets its own AES-256 data key and the content is sealed with Fernet — zero plaintext persistence
API tokens
SHA-256 hashed, show-once creation, configurable expiry, instant revocation
Execution safety
Single-use JTI tokens, replay prevention, approval gates for all write operations
Webhook signing
HMAC-SHA256 per-subscription signing secrets
Rate limiting
Per-IP and per-route limits with elevated thresholds for compute-heavy endpoints
Audit trail
Immutable action and decision logging with actor, timestamp, and payload details
Compliance
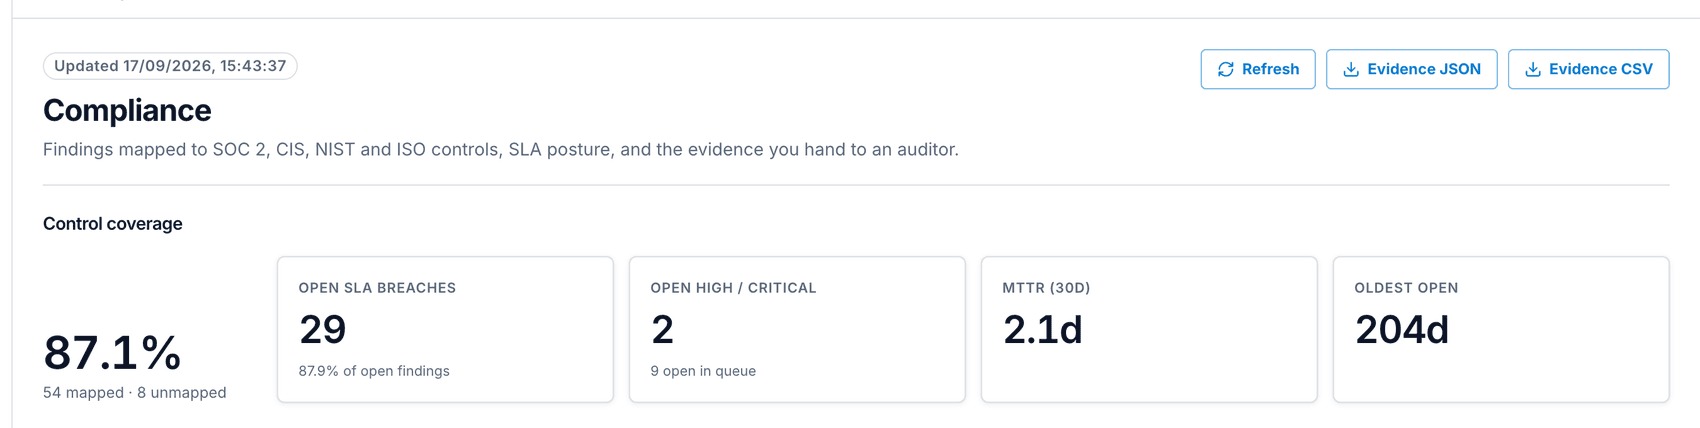
Findings mapped to controls in 8 frameworks, including SOC 2, CIS, PCI DSS, ISO 27001 and NIST 800-53, with evidence export
Encryption
Encryption at every layer
Credential handling
Provider-specific trust models
AWS, Azure, GCP, and OCI are handled differently, but every path avoids plaintext exposure and keeps execution behind approval gates.
Access control
Dual-layer RBAC
Page-level visibility and action-level permissions — independently configurable per role.
Identity and access
Who can sign in, from where, and how
Access follows your directory, and automation gets its own identities instead of borrowing a person’s.
Single sign-on
OIDC and SAML 2.0 with signed assertion validation. Identity provider discovery by email domain routes each person to the right provider. Enterprise plan.
SCIM provisioning
Your identity provider creates, updates and deactivates accounts, with group-to-role mapping and a bearer token you can rotate or revoke. Enterprise plan.
Sign-in policy
Turn SSO on, require it for everyone, require two-factor authentication, and decide whether a first sign-in creates an account.
Two-factor for administrators
Customer administrator two-factor authentication is on by default in production, with a 14-day grace window. Sessions started through enterprise SSO are exempt because your identity provider owns that factor.
Network access
Limit sign-ins, sessions and API tokens to approved office or VPN networks.
Service accounts
Non-human identities for automation and Terraform. Roles decide what they can reach and each scoped API key decides what it can call. API tokens are hashed and shown once.
Compliance
SOC 2 readiness framework
Findings mapped to eight SOC 2 Trust Services Criteria controls. Mapping supports evidence collection; it is not a certification.
Logical access controls
Findings on access restrictions that protect information and limit access to identified users
Credential lifecycle
Findings on unused, old or unrotated credentials and keys
Role-based access
Findings on roles and permissions broader than needed
Boundary protection
Findings on resources and network paths exposed outside your boundary
Vulnerability detection
Findings on detection and remediation of vulnerable configuration
Anomaly monitoring
Findings on the logging and monitoring needed to spot anomalies
Change management
Findings on controls over configuration change
Recovery infrastructure
Findings on backups, deletion protection and recovery readiness
Vs. alternatives
How we compare
The only option in this comparison that combines AI operations, commitment purchasing, policy enforcement, and governed remediation in one product.
Scroll sideways to see every column.
| Capability | CloudHealth | Infracost | Kubecost | Varcio |
|---|---|---|---|---|
| Multi-Cloud Spend | — | — | ||
| Pre-Merge PR Analysis | — | — | ||
| K8s Cost Attribution | — | — | ||
| AI Conversational Interface | — | — | — | |
| Automated Remediation | limited | — | — | |
| Commitment Purchasing | — | — | — | |
| Predictive Forecasting | basic | — | basic | |
| ChatOps Approvals | — | — | — | |
| Event Bus / Webhooks | limited | — | — | |
| Policy Engine | basic | basic | — | |
| Starting Price | $$$$ | Free (limited) | Free (limited) | $49/mo |
Security FAQs
Does Varcio store our cloud credentials?
AWS uses IAM AssumeRole, so no static access keys are stored. Azure Service Principal secrets, Google Cloud service account keys and OCI API signing keys are stored with AWS KMS envelope encryption, where each record gets its own AES-256 data key and the content is sealed with Fernet. They are never exposed in logs, API responses, or the UI.
What data do you access?
Cost, usage and billing data; commitment coverage and utilisation; resource inventory and configuration; utilisation metrics; and recommendations from each provider’s own advisors. For diagnostics, Varcio can also query exported database logs, such as slow-query and deadlock logs, through CloudWatch Logs Insights, and read query performance for databases you connect to health monitoring. Access is limited to what the credentials you grant allow.
Can auto-remediation break production?
Several safety layers apply: protected-tag exclusion, rollout-safety gates (step-up approval, a rollback success floor and maintenance windows for larger blast radius, otherwise dry run), per-rule dry-run and action caps, a maximum number of actions per run, and a monthly action budget. Requested changes need human approval. In Autopilot mode, some actions can run without a person above a confidence threshold, but resources that look production, public, critical or deletion-protected go to approval instead. Resources tagged as protected are never touched.
Are you SOC 2 certified?
The Compliance module maps findings to controls in 8 frameworks: CIS AWS, CIS Azure, CIS Google Cloud, SOC 2, PCI DSS v4.0, ISO 27001:2022, NIST 800-53 Rev. 5 and Cloud Well-Architected, with evidence export. SOC 2 mappings cover CC6.1–CC6.3, CC6.6, CC7.1, CC7.2, CC8.1 and A1.2. Mapping findings to controls is not a certification. Formal certification is in progress.
How do you handle data residency?
Cost data is processed and stored in the region you choose during onboarding. Enterprise plans support custom data residency requirements.
What happens if you have a breach?
Because AWS uses AssumeRole and Azure, GCP and OCI credentials are envelope-encrypted with strict exposure controls, the blast radius is limited to the data and write permissions you have granted. Incident response, notification, and immutable audit trails support forensic review.
Secure. Compliant. Ready.
Start your free trial with enterprise-grade security from day one.